Every email your client sent, received, or deleted tells more of the story than what appears in the inbox. The question is whether anyone has looked at the right parts of it.
Cyber Agents, Inc. conducts forensic-level email analysis for civil and criminal matters, corporate investigations, and fraud cases — documented in more than 370 engagements across Gmail, Outlook, Exchange, Microsoft 365, Google Workspace, and major cloud providers. We find content that user searches miss, establish the true origin and integrity of messages, and produce email evidence in a format that holds at deposition and at trial.
The header: every email’s audit trail
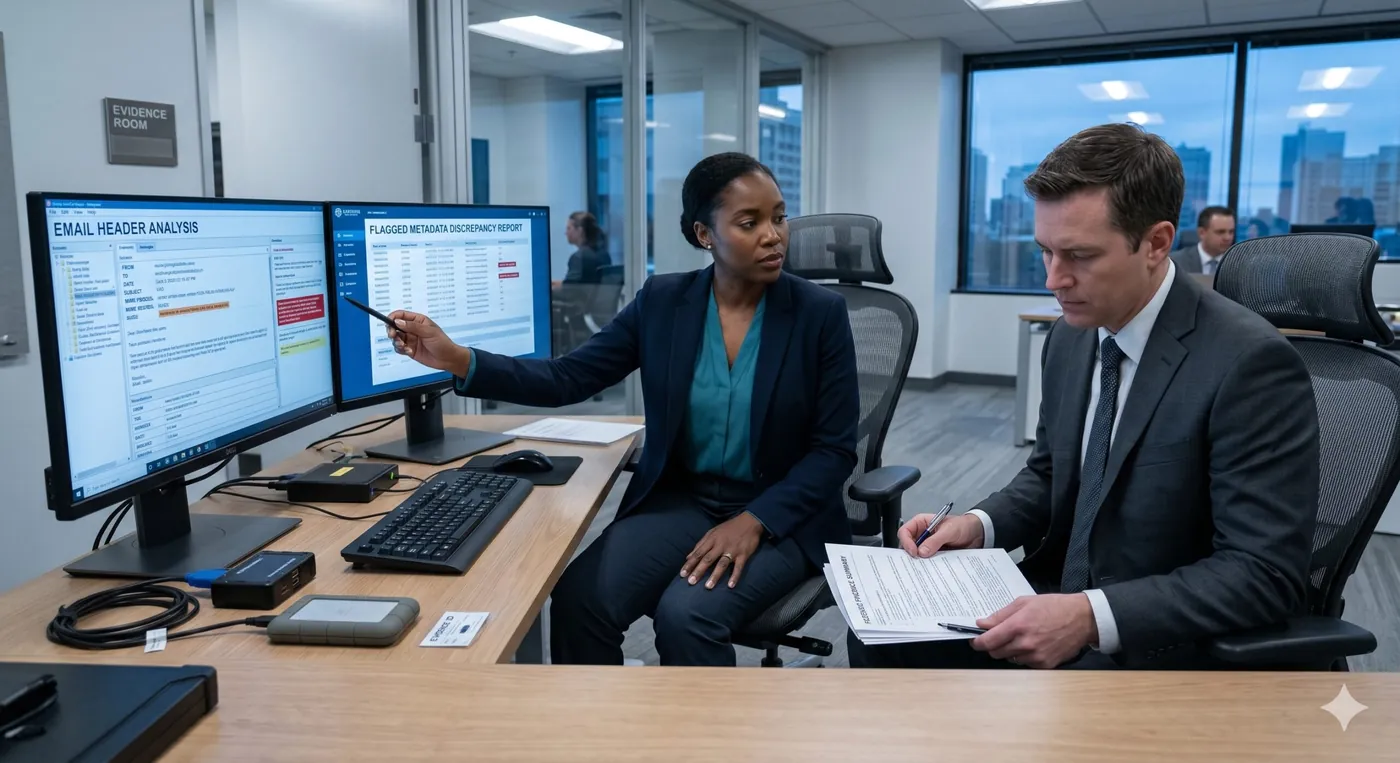
When an email travels from one inbox to another, it does not travel as a single clean message. It passes through a series of mail servers, and each server that handles the message appends a record of the handoff to the email’s header. An email header may record originating or relay information, timestamps, and authentication results, but completeness varies because mail systems can add, omit, or obscure fields.
Most email clients hide the header entirely. What a user sees in their inbox is the sender name, the subject line, and the body. Headers can provide valuable routing and authentication evidence, but they must be evaluated in context because fields can be missing, forged, altered, or stripped, and not every alteration is necessarily detectable from the message alone.
In fraud cases, the header is often the document that resolves the central question. Header and authentication data may help identify whether a message used a spoofed or look-alike domain and can support an assessment of its likely origin.
SPF and DKIM — what they mean in plain language
Two authentication standards added to email over the past decade give forensic examiners additional tools for establishing whether a message is genuine: SPF and DKIM.
SPF stands for Sender Policy Framework. Every organization that operates email can publish a list of the mail servers authorized to send messages on their behalf. When an email arrives claiming to be from a particular domain, the receiving server checks that list. If the server that sent the email is not on the authorized list, the message fails SPF verification. A message that fails SPF did not come from the infrastructure that legitimately controls the claimed sending domain.
DKIM stands for DomainKeys Identified Mail. When a mail server sends a message, it applies a cryptographic signature to the email using a private key the organization controls. The receiving server verifies that signature against a public key published in the sender’s DNS records. If the signature matches, the email demonstrably came from a server with access to the organization’s private key, and the content of the message was not changed after it was signed. If the signature fails, the email was either sent by an unauthorized source or modified after it left the sender’s server.
Together, SPF and DKIM answer two different questions. SPF addresses whether the sending server was authorized to send for that domain. DKIM addresses whether the specific message content arrived intact from a legitimate source. An email that passes both checks has a documented claim to authenticity. An email that fails one or both raises questions the header data helps answer.
What forensic collection surfaces that searches miss
Attorneys who ask their clients to search their own email and produce the results are not getting a forensic collection. They are getting whatever the email client’s search function returns — and those are not the same thing.
Email client searches — Outlook, Gmail, Apple Mail — are built for speed and user convenience. They index messages for fast retrieval, but they are not designed to be authoritative or exhaustive. They can miss messages in archive states, messages in compliance holds, messages with unusual formatting or encoding, and content in attachments that was not indexed. They do not search across every folder and hidden container in the mailbox. They return results that satisfy a user looking for a specific email they remember sending. They are not designed to find evidence.
We have collected email from clients who had already searched and found nothing relevant, then conducted a forensic review of the underlying mailbox data and recovered significant content. The messages were present. The user-level search did not surface them.
A forensic email collection pulls the entire mailbox at the data level — not through the email client’s interface, but from the underlying message store or directly from the cloud compliance environment. Every message, every folder, every hidden container. That dataset is then searched with forensic tools designed to find content, not to serve up a quick result.
What the email record shows
Email forensics has produced decisive evidence across a range of case types. In business email compromise fraud, header analysis traced the origin of a spoofed message to an unauthorized server and established that the email would have failed SPF verification at a properly configured receiving server. In employment and corporate disputes, forensic collection recovered messages the custodian had deleted, along with the timestamps of when each deletion occurred. In personal injury and wrongful death matters, internal email threads predating an incident documented that the risk was known and not addressed.
The smoking gun in an email case is often not the message anyone remembered to look for. It is the message that did not appear in the user’s search because it was archived, or deleted, or stored in a folder the user had forgotten existed.
Case types we handle
- Business email compromise and wire fraud cases requiring header analysis, SPF and DKIM verification, and origin tracing
- Corporate litigation where forensic email collection recovers content user searches did not surface
- Employment and whistleblower matters requiring complete mailbox collection and deleted message recovery
- Internal investigations where email is the primary record of what was communicated and when
- Contract disputes where the email record establishes what was disclosed, agreed to, or concealed
- Personal injury and liability matters where internal communications document prior knowledge of a hazard
Why you need an expert
An attorney who relies on a client’s self-collected email production is working with an incomplete record. An attorney who does not understand what the header data in an opposing party’s email actually shows may miss the evidence that undermines it.
Cyber Agents has analyzed email in federal court, state court, and corporate arbitration proceedings. We collect email from any provider, conduct forensic-level analysis of message content and metadata, and produce reports and testimony that explain technical findings to a lay audience. When the email record matters to the outcome of a case, a user-level search is not sufficient and a forensic examiner is not optional.
Related services and litigation support
- Cloud Forensics
- eDiscovery — O365 and Beyond
- Employment Litigation
- Corporate Espionage / Insider Threat
Contact Cyber Agents to discuss whether email forensics fits your matter.